What VIEW SERVER STATE Is For
VIEW SERVER STATE is the server-level permission that lets a login read the dynamic management views. It shows what the server is doing rather than what it holds: sessions, running requests, waits, connections, query plans and memory. It is read-only. It changes nothing and reads no user data.
The reason it surprises people is that db_datareader, db_owner, even full control of a database, grant none of it. Server state is a server-level permission and database roles cannot reach it.
You grant it to the logins that need to look at the instance without owning it:
- Monitoring tools and their service accounts, which read waits, sessions and counters on a schedule.
- DBAs and support staff who are not sysadmin, running health checks and live troubleshooting queries.
- Migration and replication tools. The AWS DMS premigration assessment checks the source login for it.
- DBA script libraries. Most of the DBA Scripts here read DMVs that need it.
How often you grant it: rarely, and once per login per instance. It comes up when a new monitoring tool, service account or DBA is set up, on every replica of an Availability Group because server permissions do not travel between instances, and again when a login is dropped and recreated. Members of sysadmin never need it.
On this page
Who Has VIEW SERVER STATE
A filter on VIEW SERVER STATE alone misses most of the people who have it. A login can get it through a direct grant, a built-in server role, ALTER SERVER STATE, CONTROL SERVER or sysadmin, and on SQL Server 2022 and later it can hold just one half of it. This lists every route in one result, says how much each one covers, and flags a DENY that cancels it:
-- Who has VIEW SERVER STATE, or half of it, and how they got it
WITH routes AS (
    SELECT pe.grantee_principal_id AS principal_id,
           'GRANT ' + pe.permission_name COLLATE DATABASE_DEFAULT AS how,
           CASE pe.permission_name
                WHEN 'VIEW SERVER PERFORMANCE STATE' THEN 'performance DMVs only'
                WHEN 'VIEW SERVER SECURITY STATE' THEN 'security DMVs only'
                ELSE 'all of VIEW SERVER STATE'
           END AS covers
    FROM sys.server_permissions AS pe
    WHERE pe.state IN ('G', 'W')
      AND pe.permission_name IN ('VIEW SERVER STATE', 'VIEW SERVER PERFORMANCE STATE',
                                 'VIEW SERVER SECURITY STATE', 'ALTER SERVER STATE', 'CONTROL SERVER')
    UNION ALL
    SELECT rm.member_principal_id,
           'member of ' + r.name COLLATE DATABASE_DEFAULT,
           CASE r.name
                WHEN '##MS_ServerPerformanceStateReader##' THEN 'performance DMVs only'
                WHEN '##MS_ServerSecurityStateReader##' THEN 'security DMVs only'
                ELSE 'all of VIEW SERVER STATE'
           END
    FROM sys.server_role_members AS rm
    JOIN sys.server_principals AS r ON r.principal_id = rm.role_principal_id
    WHERE r.name IN ('sysadmin', '##MS_ServerStateReader##',
                     '##MS_ServerPerformanceStateReader##', '##MS_ServerSecurityStateReader##')
)
SELECT p.name AS principal_name,
       p.type_desc,
       ro.how,
       ro.covers,
       CASE WHEN ro.how <> 'member of sysadmin' AND EXISTS (
                SELECT 1
                FROM sys.server_permissions AS d
                WHERE d.state = 'D'
                  AND d.permission_name = 'VIEW SERVER STATE'
                  AND (d.grantee_principal_id = p.principal_id
                       OR d.grantee_principal_id IN (SELECT m.role_principal_id
                                                     FROM sys.server_role_members AS m
                                                     WHERE m.member_principal_id = p.principal_id)))
            THEN 'yes' ELSE '' END AS deny_found
FROM routes AS ro
JOIN sys.server_principals AS p ON p.principal_id = ro.principal_id
ORDER BY p.name;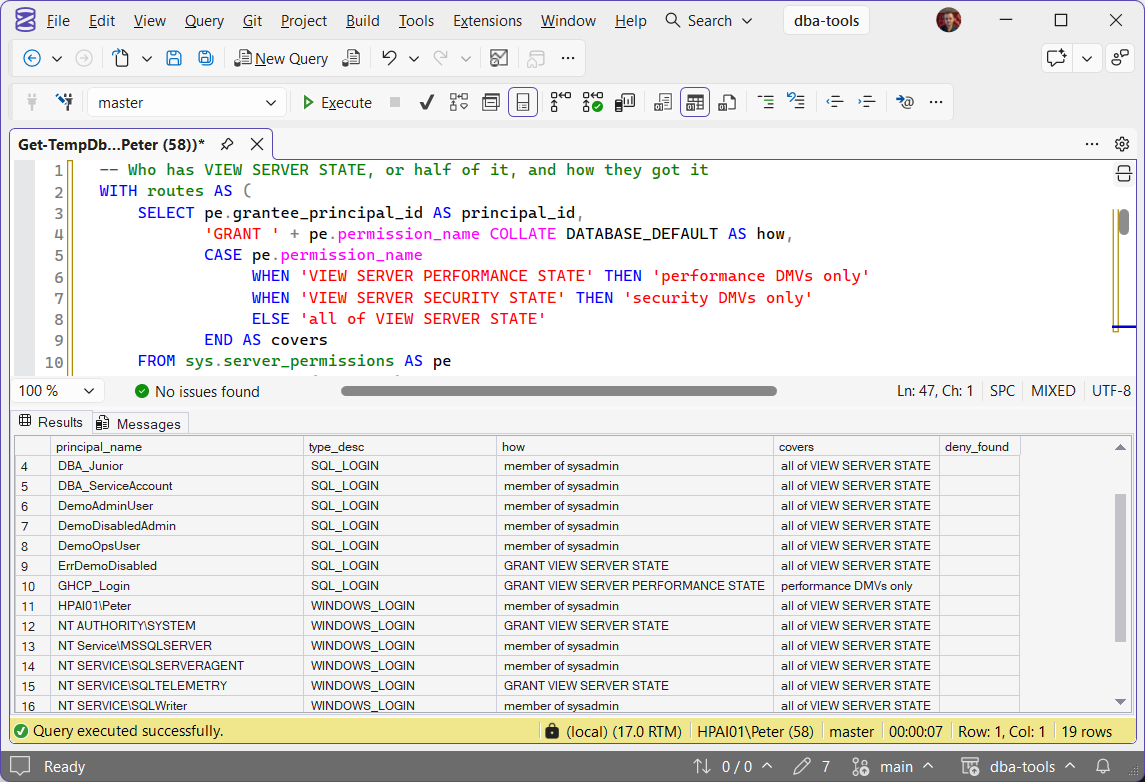
On my lab instance it returns 19 rows: the sysadmin members, the logins granted VIEW SERVER STATE directly, and GHCP_Login, which holds only VIEW SERVER PERFORMANCE STATE. Read the columns like this:
coverssays performance DMVs only for a login holding justVIEW SERVER PERFORMANCE STATE. It can read waits and requests, but it does not haveVIEW SERVER STATEitself.deny_foundis yes when aDENY VIEW SERVER STATEsits on the login or on a server role it belongs to. That login is listed with a grant and still cannot read the DMVs.- Windows users who get it through a group appear as the group, so check group membership for the person.
The COLLATE DATABASE_DEFAULT is there because the permission names and the role names come back in different collations on some instances, and the UNION ALL fails with Msg 451 without it. The 2022 permission and role names are plain text in the filter, so on SQL Server 2019 and earlier they simply match nothing.
Check One Login
For a single login, ask SQL Server for the effective answer. This is the quickest way to confirm a service account, an AWS DMS login for example, has what it needs before you hand it over. It needs IMPERSONATE on the login, or sysadmin:
-- One login, the effective answer
EXECUTE AS LOGIN = 'the_login';
SELECT SUSER_NAME() AS login_name,
       HAS_PERMS_BY_NAME(NULL, NULL, 'VIEW SERVER STATE') AS has_view_server_state,
       HAS_PERMS_BY_NAME(NULL, NULL, 'VIEW SERVER PERFORMANCE STATE') AS has_view_server_performance_state;
REVERT;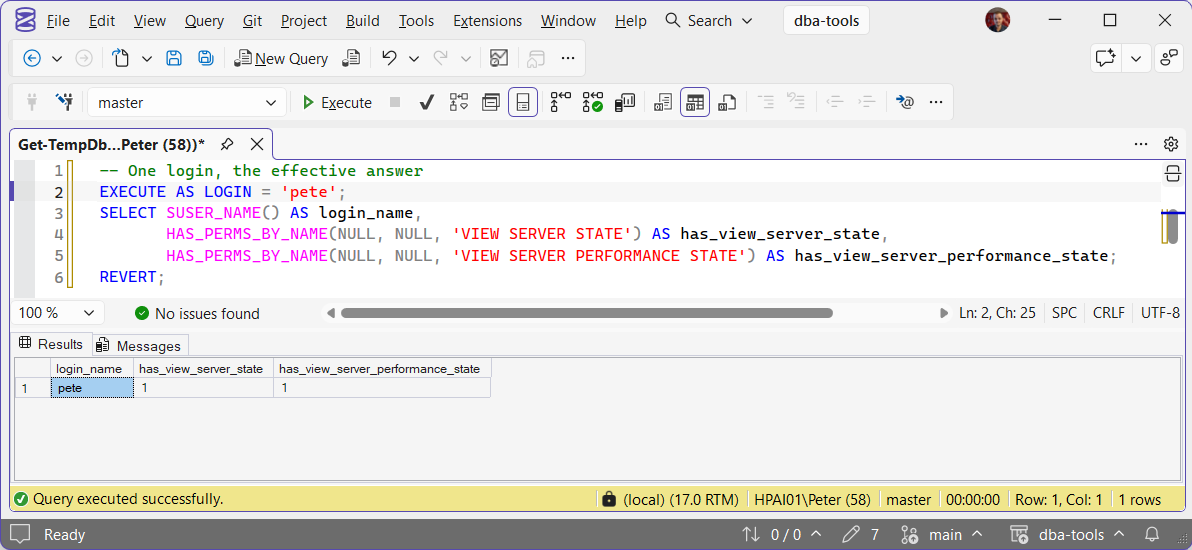
Run as pete, a login granted VIEW SERVER STATE, both columns return 1, because VIEW SERVER STATE covers the performance half too. A login holding only VIEW SERVER PERFORMANCE STATE returns 0 then 1, and a login with a DENY returns 0 for both, whatever it was granted.
Related State Permissions, Server and Database
SQL Server 2022 split server state into two halves, and each database has its own matching set. Database-level grants are made inside one database and cover only that database. This is how they sit, read from sys.fn_builtin_permissions on SQL Server 2025:
| Permission | Scope | Also granted by |
|---|---|---|
VIEW SERVER STATE | Instance | ALTER SERVER STATE, CONTROL SERVER |
VIEW SERVER PERFORMANCE STATE | Instance, SQL Server 2022 and later | VIEW SERVER STATE |
VIEW SERVER SECURITY STATE | Instance, SQL Server 2022 and later | VIEW SERVER STATE |
VIEW DATABASE STATE | One database | CONTROL on the database, or VIEW SERVER STATE |
VIEW DATABASE PERFORMANCE STATE | One database, SQL Server 2022 and later | VIEW DATABASE STATE, or VIEW SERVER PERFORMANCE STATE |
VIEW DATABASE SECURITY STATE | One database, SQL Server 2022 and later | VIEW DATABASE STATE, or VIEW SERVER SECURITY STATE |
This lists every state grant and DENY in one result: the server-level ones, then the database-level ones in every online database you can open, with the login each database user maps to:
-- Every server and database state grant on the instance, one result
DECLARE @sql nvarchar(max) = N'';

SELECT @sql = @sql + N'
UNION ALL
SELECT ' + QUOTENAME(d.name, '''') + N' COLLATE DATABASE_DEFAULT,
       dp.name COLLATE DATABASE_DEFAULT,
       ISNULL(sp.name, ''(no login)'') COLLATE DATABASE_DEFAULT,
       pe.state_desc + '' '' + pe.permission_name COLLATE DATABASE_DEFAULT
FROM ' + QUOTENAME(d.name) + N'.sys.database_permissions AS pe
JOIN ' + QUOTENAME(d.name) + N'.sys.database_principals AS dp ON dp.principal_id = pe.grantee_principal_id
LEFT JOIN sys.server_principals AS sp ON sp.sid = dp.sid
WHERE pe.class = 0
  AND pe.permission_name IN (''VIEW DATABASE STATE'', ''VIEW DATABASE PERFORMANCE STATE'', ''VIEW DATABASE SECURITY STATE'')'
FROM sys.databases AS d
WHERE d.state_desc = 'ONLINE'
  AND HAS_DBACCESS(d.name) = 1;

SET @sql = N'
SELECT N''(server)'' COLLATE DATABASE_DEFAULT AS scope,
       pr.name COLLATE DATABASE_DEFAULT AS principal_name,
       pr.name COLLATE DATABASE_DEFAULT AS login_name,
       pe.state_desc + '' '' + pe.permission_name COLLATE DATABASE_DEFAULT AS permission
FROM sys.server_permissions AS pe
JOIN sys.server_principals AS pr ON pr.principal_id = pe.grantee_principal_id
WHERE pe.permission_name IN (''VIEW SERVER STATE'', ''VIEW SERVER PERFORMANCE STATE'', ''VIEW SERVER SECURITY STATE'')'
    + @sql + N'
ORDER BY scope, principal_name;';

EXEC sys.sp_executesql @sql;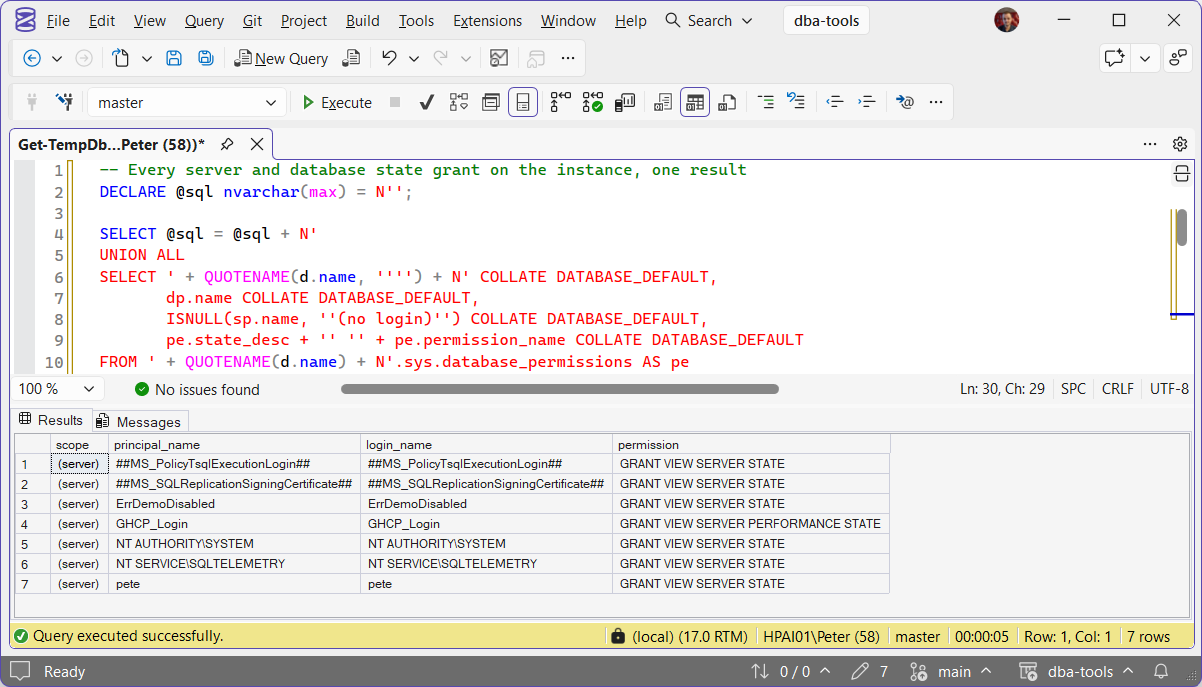
On my lab instance every row is server-level, because no database there holds a state grant. Where one does, it shows with the database name in scope, for example a migration login that only needs one database. That is the narrowest grant there is: VIEW DATABASE PERFORMANCE STATE in the one database a tool reads, instead of server-wide state.
Grant VIEW SERVER STATE
GRANT VIEW SERVER STATE TO [DOMAIN\your_login];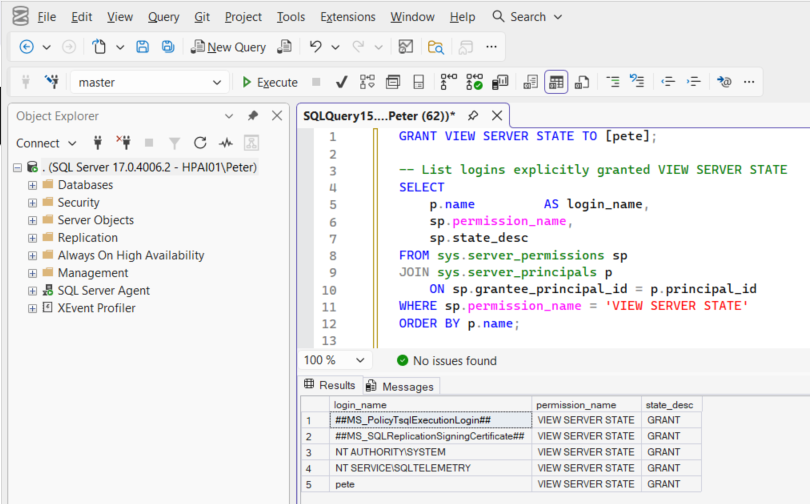
For a monitoring account, this is usually the right minimum set:
GRANT VIEW SERVER STATE TO [DOMAIN\monitoring_account]; -- DMVs
GRANT VIEW ANY DEFINITION TO [DOMAIN\monitoring_account]; -- object definitions
GRANT CONNECT SQL TO [DOMAIN\monitoring_account];
Do not solve this with sysadmin. It is the reflex, it works, and it hands over the entire instance to something that only needed to read a DMV.
On SQL Server 2022 and later there are 2 narrower options. Grant only the half the login needs, or add it to one of the built-in server roles, which is the easier thing to audit:
-- SQL Server 2022 and later: the performance half only (waits, requests, plans)
GRANT VIEW SERVER PERFORMANCE STATE TO [DOMAIN\monitoring_account];

-- Or the built-in role that carries VIEW SERVER STATE
ALTER SERVER ROLE [##MS_ServerStateReader##] ADD MEMBER [DOMAIN\monitoring_account];
##MS_ServerPerformanceStateReader## and ##MS_ServerSecurityStateReader## are the role versions of the 2 halves.
Microsoft’s reference covers GRANT Server Permissions in full, including which of the 2022 permissions sits under which.
If You Landed Here From the Error
You hit this the moment you query a DMV without the permission. On SQL Server 2022 and later the message names the half the DMV needs: VIEW SERVER PERFORMANCE STATE for waits and requests, as in the screenshot, and VIEW SERVER SECURITY STATE for the security DMVs. On SQL Server 2019 and earlier it names VIEW SERVER STATE. Granting VIEW SERVER STATE fixes all three.
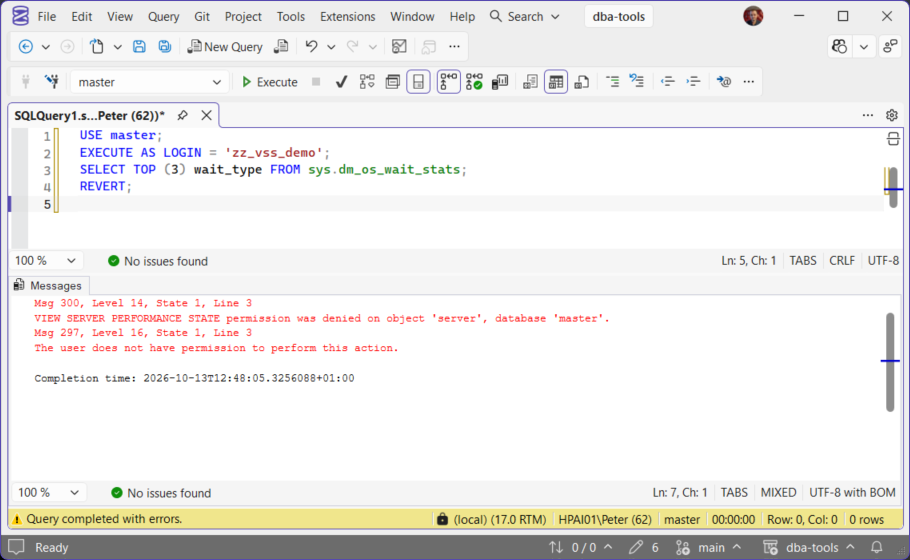
To see what your own login holds right now:
-- What am I, and what am I allowed to do at server level?
SELECT SUSER_NAME() AS login_name,
       IS_SRVROLEMEMBER('sysadmin') AS is_sysadmin,
       HAS_PERMS_BY_NAME(NULL, NULL, 'VIEW SERVER STATE') AS has_view_server_state,
       HAS_PERMS_BY_NAME(NULL, NULL, 'VIEW SERVER PERFORMANCE STATE') AS has_view_server_performance_state,
       HAS_PERMS_BY_NAME(NULL, NULL, 'VIEW ANY DEFINITION') AS has_view_any_definition;
has_view_server_state returning 0 is your answer, with one catch on SQL Server 2022 and later: a login granted only VIEW SERVER PERFORMANCE STATE reads the performance DMVs fine but still shows 0 there, so check the next column too.
No error, just 1 row. Several DMVs return only your own session when you lack the permission, instead of failing. If sys.dm_exec_requests shows 1 row on a busy server, it is a permissions problem, not an idle instance.
The One That Catches Everyone: DENY
If a GRANT appears to do nothing, look for a DENY, including one inherited from a Windows group the login belongs to. DENY always beats GRANT, no matter which is more specific or which came last. The one exception is a member of sysadmin: SQL Server skips permission checks for it entirely, so a DENY on a sysadmin login does nothing.
A DENY VIEW SERVER STATE also blocks both SQL Server 2022 halves underneath it, so the login fails with Msg 300 whatever else it was granted. The deny_found column in the who has it query flags it.
-- Any DENY that could be overriding the grant, direct or via a group
SELECT pr.name AS principal_name, pr.type_desc, pe.permission_name, pe.state_desc
FROM sys.server_permissions AS pe
JOIN sys.server_principals AS pr ON pr.principal_id = pe.grantee_principal_id
WHERE pe.state_desc = 'DENY'
  AND pe.permission_name IN ('VIEW SERVER STATE', 'CONNECT SQL');
Remove it rather than layering another grant on top:
REVOKE VIEW SERVER STATE FROM [DOMAIN\the_group];
GRANT VIEW SERVER STATE TO [DOMAIN\your_login];
Azure SQL Database Is Different
In Azure SQL Database there is no GRANT VIEW SERVER STATE. For one database, grant the database-level equivalent inside it. For the server-wide DMVs, add the login to ##MS_ServerStateReader## in master.
GRANT VIEW DATABASE STATE TO [your_user];Managed Instance behaves like the boxed product and uses VIEW SERVER STATE.
Stopping It Recurring
Give monitoring its own server role. When more than one tool or team needs to read the instance, create the role once, grant it the permissions, and add logins and AD groups as members. New starters and new tools then get one membership instead of a set of individual grants.
CREATE SERVER ROLE monitoring_readers;
GRANT VIEW SERVER STATE TO monitoring_readers;
GRANT VIEW ANY DEFINITION TO monitoring_readers;

-- SQL logins and AD groups can both be members
ALTER SERVER ROLE monitoring_readers ADD MEMBER [monitoring_tool_login];
ALTER SERVER ROLE monitoring_readers ADD MEMBER [DOMAIN\DBA-Monitoring];
It has to be a server role. VIEW SERVER STATE is a server permission, and a database role cannot hold one: the grant fails with Msg 15151 in master and Msg 4621 anywhere else. Tested on SQL Server 2025, a member of this role read the waits DMVs and held both permissions.
Or use a built-in role. SQL Server 2022 added 10 fixed server roles with the ##MS_ prefix, and SQL Server 2025 ships the same set. For a monitoring tool, ##MS_ServerPerformanceStateReader## is the narrow fit, plus ##MS_PerformanceDefinitionReader## if it also needs VIEW ANY PERFORMANCE DEFINITION.
Either way, server roles live on each instance, so repeat the setup on every Availability Group replica.
Audit for DENY after any security review. Hardening passes add denies that surface weeks later as this error.
Frequently Asked Questions
How often do you need to grant VIEW SERVER STATE?
How do I see who has VIEW SERVER STATE?
Can I give it to a database role?
Is VIEW SERVER STATE safe to grant?
I granted it and nothing changed.
sysadmin member.The DMV returns 1 row instead of the whole instance.
The message says VIEW SERVER PERFORMANCE STATE, not VIEW SERVER STATE. Which do I grant?
VIEW SERVER STATE into two narrower children, VIEW SERVER PERFORMANCE STATE for the performance DMVs and VIEW SERVER SECURITY STATE for the security ones, and the denial now names the one the DMV needs. GRANT VIEW SERVER STATE covers both; grant the narrower one when the login genuinely only needs that half.Where To Go Next
VIEW SERVER STATE is the permission most monitoring scripts need. Once it is granted, these are what you run.
- Login Failed or Permission Denied, the router for when the denial is not VIEW SERVER STATE.
- Get Permissions and Role Membership, one login’s effective access across the instance, including this grant.
- Get Sysadmin Members, who holds the keys, and the reason not to add another one.
- Get Wait Statistics, one of the many things this permission unlocks.
- SQL Server Security Scripts, permissions, logins and role membership auditing.
- DBA Scripts, the full script library, most of which needs this permission.
Leave a Reply